What Wireless Penetration Testing Is
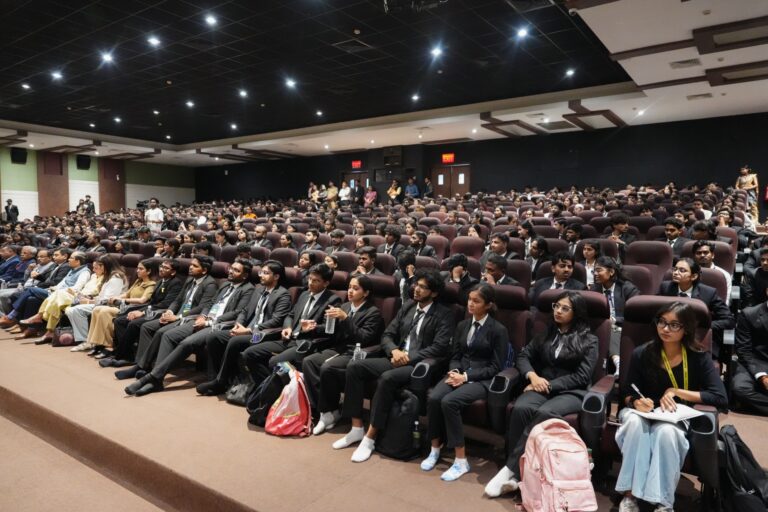
Every wireless network broadcasts its presence, which makes Wi-Fi both convenient and exposed. At a session during “Talktime with Lakshya 2047” at Parul University, Mr. Mohit Soni, Founder of Lancer InfoSec and a penetration tester with more than fifty security assessments behind him, walked students through wireless penetration testing: the authorised, methodical assessment of how secure a wireless network really is. His central message was that it begins not with attacks but with understanding.
Reconnaissance is one of the most important phases of penetration testing, because you cannot secure what you do not understand.
– Mr. Mohit Soni, Lancer InfoSec
Wireless penetration testing is an organised, maintained and authorised evaluation of a wireless network’s security. Rather than attempting attacks, a process is followed that is professional, and it has a methodology, planning, reconnaissance, vulnerability identification, controlled and permitted testing, analysis of impact and making reports of it to find the authentication mechanisms, encryption, access-point configuration, signal exposure, rogue devices, and client security. The goal is not to break the security, but to find out the weakness before any real attack happens and find the solution to protect the organisation.
Basics of Wi-Fi in Brief
Wireless networks work through Access Points (APs) and the client devices that connect to them. Each network broadcasts an identifier known as Service Set Identifier (SSID) so other nearby devices can find it, and communication happens across defined frequency bands. Understanding how wireless devices are meant to communicate is the necessary foundation, because you cannot meaningfully assess a system’s security until you understand how it is supposed to work.
The Evolution of Wi-Fi Encryption: WEP, WPA, WPA2, WPA3
Most of what determines a wireless network’s safety comes down to its encryption standard, and these have improved markedly over time:
- WEP: the earliest standard, now obsolete. It contains serious cryptographic weaknesses that allow encryption keys to be recovered quickly, and it should never be used in modern deployments.
- WPA and WPA2: a major improvement, introducing stronger authentication and encryption. WPA2 remains widely used, but it is only as strong as its configuration.
- WPA3: the latest standard, offering stronger protections, including better defences for networks and improved handling of the weaknesses that affected earlier standards.
The crucial caveat, stressed throughout the session, is that encryption is not a complete defence. Even a WPA2 or WPA3 network becomes vulnerable when organisations use weak passwords, default credentials, or careless configuration. Technology and human practice have to improve together.
Strong encryption alone cannot protect a wireless network if users choose weak passwords or poor configurations.
– Mr. Mohit Soni, Lancer InfoSec
Reconnaissance, Monitor Mode, and Common Threats
A concept central to wireless assessment is monitor mode, in which a wireless adapter observes nearby wireless traffic for analysis rather than connecting to a single network. Used within an authorised assessment, it lets a professional identify access points, analyse channels, and understand the environment before evaluating its security, the reconnaissance that makes an assessment systematic rather than random. The session also explained, at a conceptual level, why certain wireless threats exist: for example, older wireless management frames were not protected, which is a weakness that modern standards like WPA3 help address. Understanding why a weakness exists is what allows an organisation to defend against it.
The Ethics and Methodology That Define a Professional
The session’s strongest theme was ethics. Any wireless testing must be performed only within authorised environments, after explicit permission from the network owner, and without disrupting legitimate users. Professional penetration testing is defined by methodology, careful observation, and analysis, followed by clear reporting that documents findings, evidence, business impact, and practical remediation, not by the indiscriminate use of tools.
Tools do not make someone a penetration tester. Knowledge, methodology, and ethics do.
– Mr. Mohit Soni, Lancer InfoSec
How to Get Into Wireless and Offensive Security
Interested students who wish to make a career in cybersecurity are advised to make their foundations strong in networking, operating systems and Linux, scripting and communication skills, along with security concepts.
Continuous, hands-on practice matters most, through Capture the Flag (CTF) competitions, bug bounty programs, security communities, and lab practice in authorised environments. Wireless security is not a single field; with modern demands and changes, professionals are required to assess web applications, cloud, and IoT as well, which are today part of the cybersecurity career paths.